
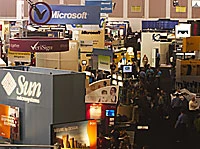
SAN JOSE, Calif., 21 February 2006 — Now in its 15th year, the RSA Conference focuses on information security and cryptography. From Feb. 13-17 in San Jose, California, some of the biggest names in the IT industry put forward their thoughts on the way forward in information security.
Microsoft Chairman Bill Gates described the weapon that he hopes will do away with passwords. Windows Vista, Microsoft’s new operating system, due later this year, introduces a concept called infocards that gives users a better way to manage the multitude of Internet login names and passwords, as well as lets third parties help in the verification process. Vista will also make it easier to log on to PCs using something stronger than a password alone, such as a smart card.
Microsoft has described infocards as a technology that gives users a single place to manage various authentication and payment information, in the same way a wallet holds multiple credit cards.
Gates’ keynote address at the 2006 RSA conference was one of the first opportunities to get an idea of how infocards might work. In the Microsoft presentation it was shown how a consumer could use a self-generated infocard to log in to a car rental site and then use a separate infocard from a membership group to get a discount on the rental.
Not everyone was as optimistic as Gates concerning the replacement of passwords with other technologies, cryptographers being perhaps the most critical. Even Gates himself didn’t think that passwords would disappear immediately.
“I don’t pretend that we are going to move away from passwords overnight, but over three or four years, for corporate systems, this change can and should happen,” he remarked.
Moving from the specific to a broader perspective, Cisco Systems CEO John Chambers used his time at the podium to present a more holistic view of security. Chambers believes that corporations should see the network as an integrated system with security coordinated across the entire network.
“Assume employees are going across a lot of networks,” he said. “So you have to build in security from the home to any number of networks. Security has to happen at the infrastructure.”
Cisco asserts that open standards are the way to go in developing security for networks. The company is also looking for ways to automate the security process on the network and to isolate attacks when they occur.
Cisco is currently working toward its Adaptive Threat Defense initiative, which calls for intelligent networks to defend themselves against attacks. As part of that effort the company has launched an aggressive seven-year plan to build out its security portfolio via acquisitions and partnerships.
Chambers’ vision is just one of several vendor plans on the table right now to deal with the numerous information security crises facing corporate networks. In his keynote address at the 2006 RSA Conference, 3Com’s Chief Technology Officer Marc Willebeek-LeMair presented 3Com’s means for solving the critical issues in enterprise networking — comprehensive network security and application performance. This new approach to networking, 3Com’s Bi-Planar Network Vision, is targeted to achieve what today’s network of switches and routers cannot — complete access control, attack control and application control.
During his presentation, Willebeek-LeMair pointed out that the pain enterprise customers experience today is directly related to the inability to control what users, devices and traffic are allowed into the network; inability to filter out malicious and unwanted traffic; and inability to prioritize and accelerate business critical applications on a converged IP network. Inadequate security and sluggish applications can severely impede businesses today. When the network stops, business stops.
Willebeek-LeMair described his vision for a Bi-Planar Network where a Control Plane is overlaid onto today’s traditional network, which he termed the Connectivity Plane. The Connectivity Plane — comprising routers and switches — simply directs traffic to its destination, but is not designed to perform the deep packet classification and policy enforcement functions required to meet network security and application performance needs.
Which method and means will enable better information security? That’s a question that each individual, company and nation must answer based on consideration of the facts. To learn more on the new directions in information security, check out all the 2006 RSA Conference keynotes mentioned here plus presentations from Sun Microsystems, Symantec, CA, the FBI and of course the cryptographers, by going to https://2006.rsaconference.com/us/conference/webcasts.aspx.